CVE-2022-2804
CVE-2022-2804 is a medium-severity vulnerability in Phpgurukul Zoo Management System with a CVSS 3.x base score of 6.3. It is not currently listed as actively exploited by CISA, and its EPSS exploit-prediction score is low. The underlying weakness is classified as CWE-434.
Key facts
- Severity: Medium (CVSS 3.x base score 6.3)
- EPSS exploit prediction: 1% (64th percentile)
- Actively exploited: Not listed in CISA KEV
- Weakness: CWE-434
- Affected product: Phpgurukul Zoo Management System
- Published:
- Last modified:
Description
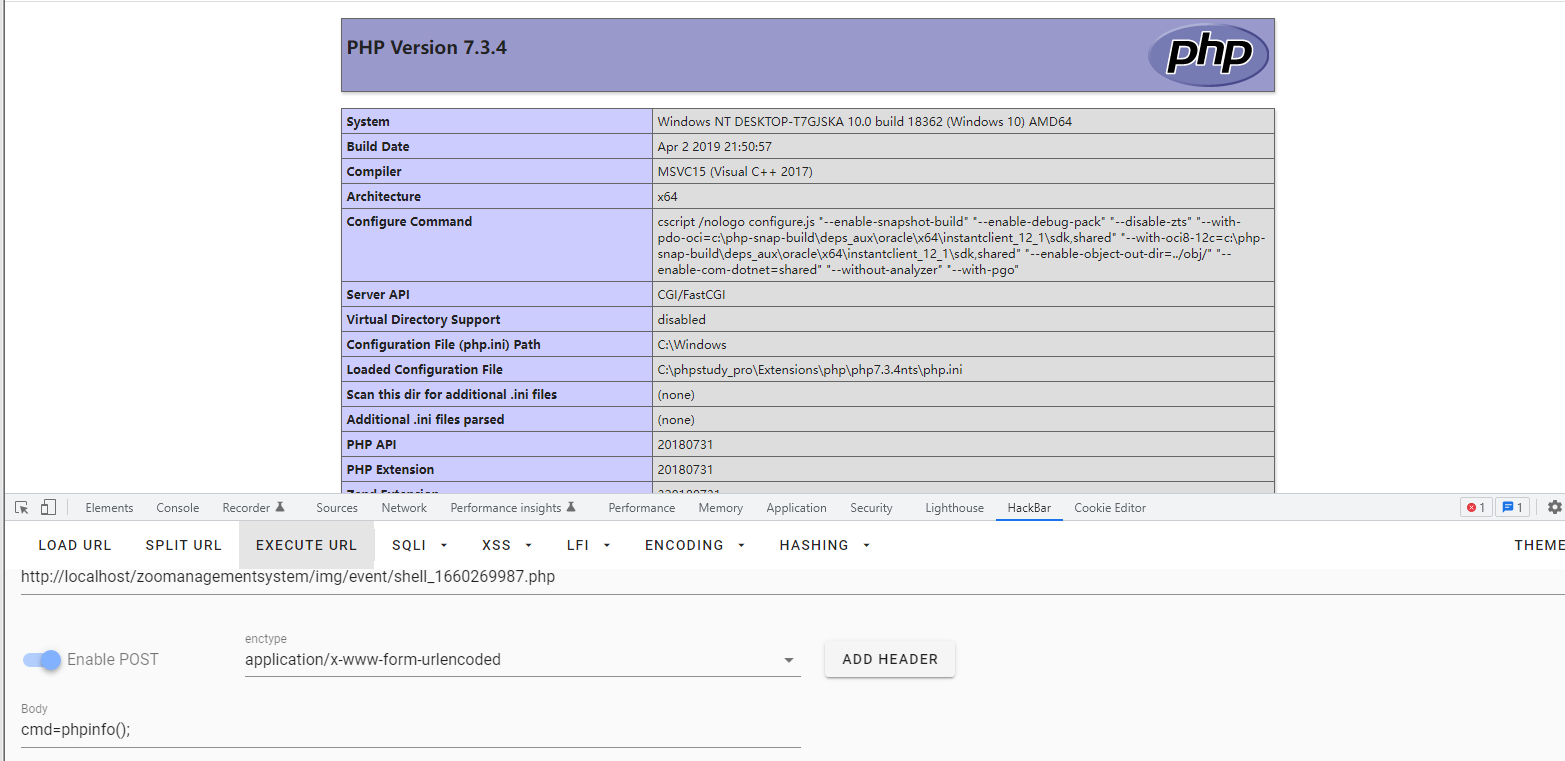
A vulnerability was found in SourceCodester Zoo Management System. It has been classified as critical. Affected is an unknown function of the file /pages/apply_vacancy.php. The manipulation of the argument filename leads to unrestricted upload. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. VDB-206250 is the identifier assigned to this vulnerability.
Frequently asked questions
- What is CVE-2022-2804?
- A vulnerability was found in SourceCodester Zoo Management System. It has been classified as critical. Affected is an unknown function of the file /pages/apply_vacancy.php. The manipulation of the argument filename leads to unrestricted upload. It is possible to launch the attack remotely. The exploit has been disclosed to the public and may be used. VDB-206250 is the identifier assigned to this vulnerability.
- How severe is CVE-2022-2804?
- CVE-2022-2804 has a CVSS 3.x base score of 6.3, rated medium severity. It is exploitable over network with low attack complexity, requires low privileges and no user interaction. Impact on confidentiality is low, integrity low, and availability low.
- Is CVE-2022-2804 being actively exploited?
- It is not currently listed in CISA's KEV catalog. Its EPSS exploit-prediction score is 1% (64th percentile), an estimate of the probability of exploitation in the next 30 days.
- What products are affected by CVE-2022-2804?
- CVE-2022-2804 affects Phpgurukul Zoo Management System. See the affected-products list for the exact vulnerable versions.
- How do I fix CVE-2022-2804?
- Review the linked vendor and NVD advisories for patched versions and mitigations, then upgrade or apply the recommended workaround.
- When was CVE-2022-2804 published?
- CVE-2022-2804 was published on 2022-08-12 and last updated on 2026-06-17.
References
Affected products (1)
- cpe:2.3:a:phpgurukul:zoo_management_system:-:*:*:*:*:*:*:*
More vulnerabilities in Phpgurukul Zoo Management System
- CVE-2024-25350 — Critical (CVSS 9.8): SQL Injection vulnerability in /zms/admin/edit-ticket.php in PHPGurukul Zoo Management System 1.0 via tickettype and…
- CVE-2023-41615 — Critical (CVSS 9.8): Zoo Management System v1.0 was discovered to contain multiple SQL injection vulnerabilities in the Admin sign-in page…
- CVE-2022-27351 — Critical (CVSS 9.8): Zoo Management System v1.0 was discovered to contain an arbitrary file upload vulnerability via…
- CVE-2022-27992 — High (CVSS 8.8): Zoo Management System v1.0 was discovered to contain a SQL injection vulnerability at /public_html/animals via the…
- CVE-2020-25487 — High (CVSS 7.8): PHPGURUKUL Zoo Management System Using PHP and MySQL version 1.0 is affected by: SQL Injection via…
- CVE-2025-7160 — High (CVSS 7.3): A vulnerability classified as critical has been found in PHPGurukul Zoo Management System 2.1. This affects an unknown…
All CVEs affecting Phpgurukul Zoo Management System →
Other CWE-434 (Unrestricted Upload of File with Dangerous Type) vulnerabilities
- CVE-2026-14914 — Critical (CVSS 10.0): Unrestricted upload of file with dangerous type vulnerability in Tegsoft Yönetim ve Bilişim Hizmetleri Tic. Ltd.…
- CVE-2026-117551 — Critical (CVSS 10.0): Joomla Extension - jdownloads.com - RCE through file upload in jDownloads < 4.1.8 - Insufficient validation of…
- CVE-2026-110469 — Critical (CVSS 10.0): WidzialniCMS is vulnerable to Unrestricted File Upload in the /panel/upload.php endpoint. Due to a client-controlled…
- CVE-2026-110468 — Critical (CVSS 10.0): WidzialniCMS is vulnerable to Unrestricted File Upload in the /panel/controllers/save_photo.php endpoint. Due to a…
- CVE-2026-118423 — Critical (CVSS 10.0): The WP Libre Form WordPress plugin 1.5.0.1 does not validate the type of files uploaded through its form submissions,…
- CVE-2026-102785 — Critical (CVSS 10.0): Joomla Extension - yootheme.com - Unauthenticated remote code execution in YOOtheme Pro 5.0.0-5.0.52 - YOOtheme Pro’s…
Browse all CWE-434 (Unrestricted Upload of File with Dangerous Type) vulnerabilities →